Okta API
This guide walks you through the process of creating a service app client in Okta.
Steps to Create a service app Client in Okta
1. Sign In to Okta
- Log in to your Okta instance as an admin.
2. Create an App Integration
- Navigate to Applications and Resources > Applications.
- Click on Create App Integration.
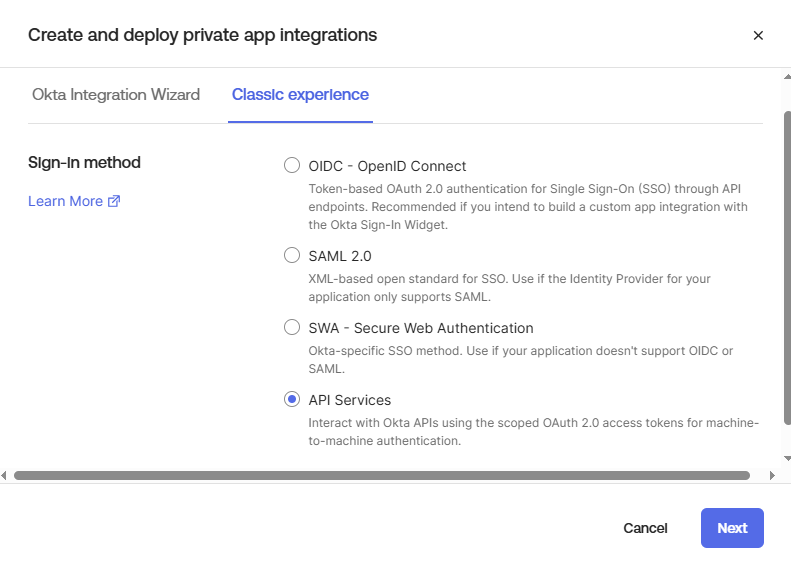
- Select the Classic Experience tab.
3. Select App Integration Type
- Choose API Services as the Sign-in Method.
4. Fill in Integration Details
- Provide an App Integration Name.
- Select Use Okta-generated client ID.
5. Save the Integration
- Click Save to create the app integration.
6. Configure your application
-
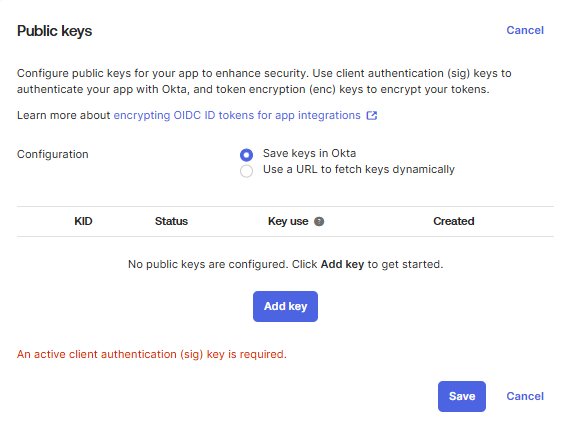
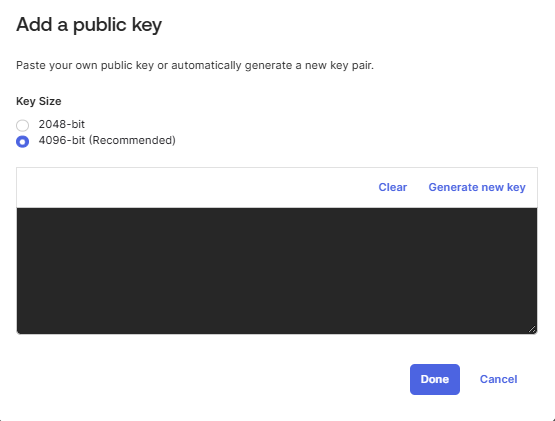
In your application's General tab, scroll down to the Public Keys section.
-
Click Add Key.
-
Click Generate New Key.
-
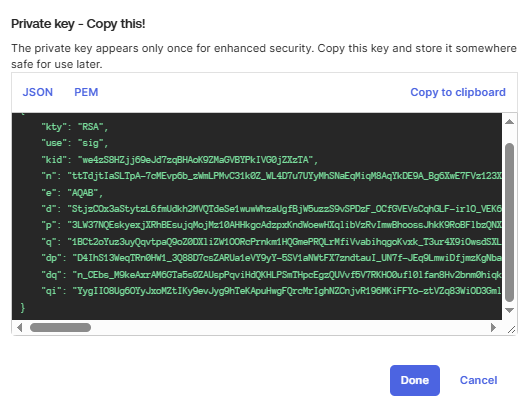
Copy the generated private key (JSON) and store it securely. This key will not be displayed again, so make sure to save it before proceeding.
-
Click Done, and then click Save.
-
You will need this private key during the integration with Knit.
-
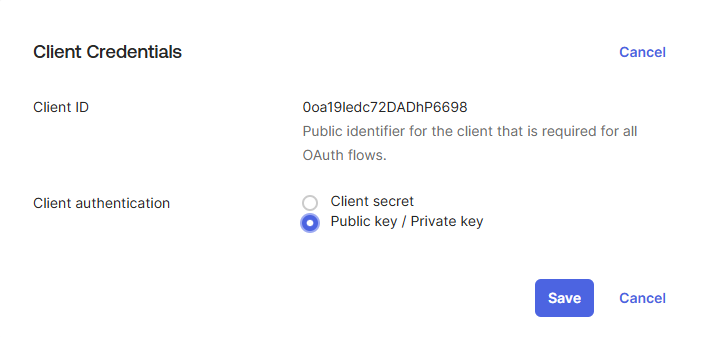
Scroll down to the Client Credentials section.
-
Select Public key / Private key as the Client Authentication method and save the changes.
-
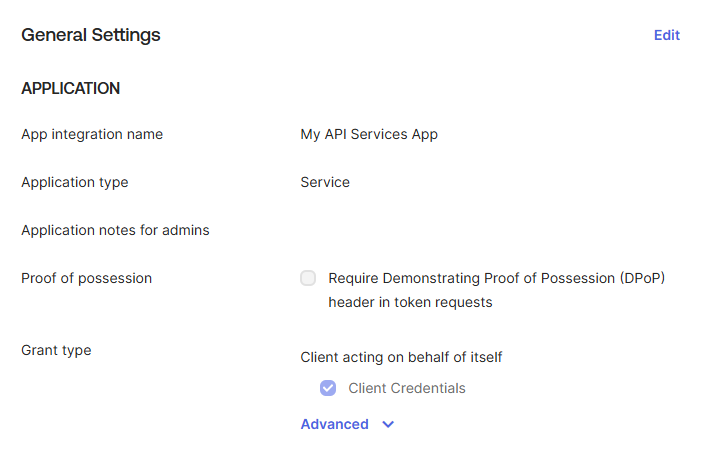
Copy the Client ID and store it securely. You will need it when configuring the integration with Knit.
-
In the General Settings section, disable Proof of Possession (DPoP).
7. Configure API Scopes
- In the Okta Admin Console, Applications and Resources > Applications and open your application.
- Go to the Okta API Scopes tab.
- Grant the following scope:
- okta.users.read
Optional: Enabling Additional Scopes with Phishing-Resistant 2FA
If you need to use APIs for creating, updating, or terminating employees, enabling the okta.users.manage scope is required. Okta recommends setting up phishing-resistant 2FA for this purpose.
Steps to Enable Phishing-Resistant 2FA
1. Update Authentication Policies
-
Navigate to Security > Authentication Policies.
-
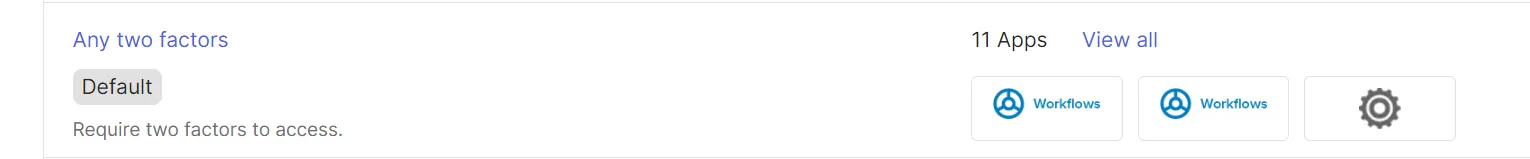
Click on the Any Two Factors policy.
-
-
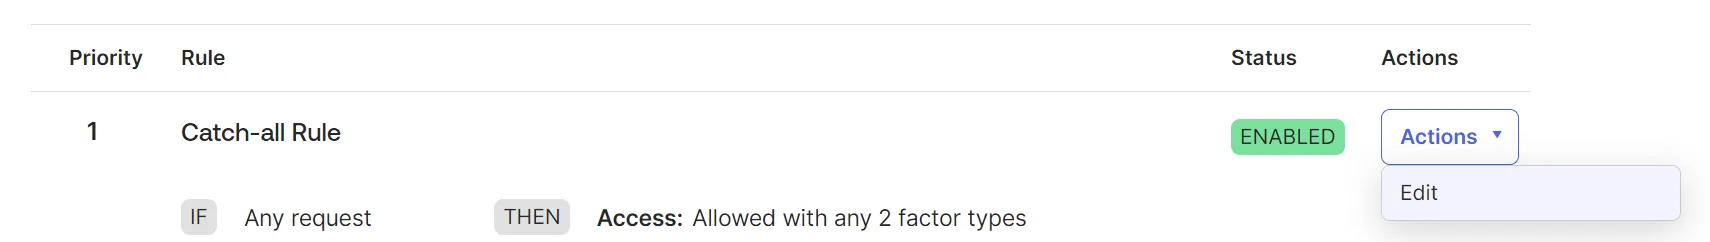
Edit the Catch-all Rule.
-
2. Set Possession Factor Constraints
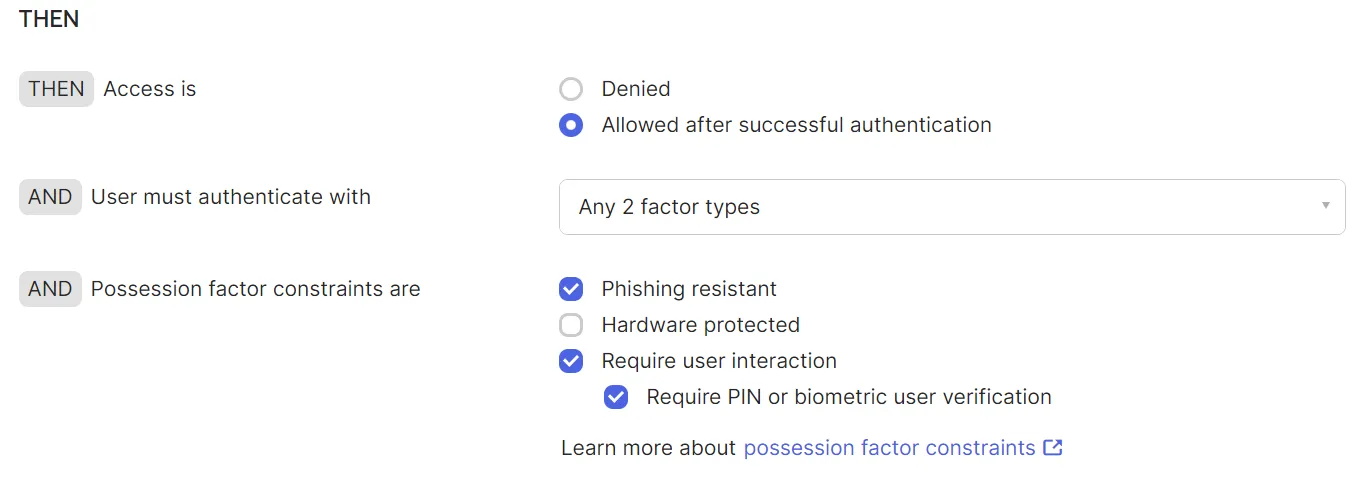
- Enable the Phishing Resistant checkbox under Possession Factor Constraints.
3. Add Phishing-Resistant Authenticator
- Navigate to Security > Authenticators.
- Add FIDO2 (WebAuthn) as an authenticator.
Final Step
- You are now set up with phishing-resistant 2FA for managing employee-related APIs.
Reference
- Video for creating the integration on Knit using the Okta client: Loom Video.
Updated about 7 hours ago